


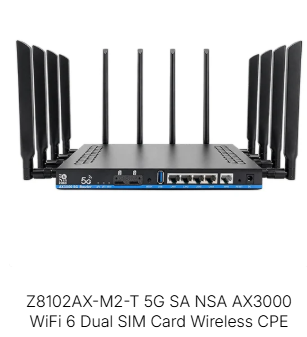
Dear Customers and Business Partners,
A major security discovery has emerged in the field of network security affecting popular routers manufactured by Zbtlink. Security analysts at VulnCheck have uncovered a critical vulnerability in the factory software of these devices that functions as a persistent backdoor.
We want to immediately reassure all our clients that your networks and devices are completely unaffected by this risk. As a trusted systems integrator and network solutions provider, we do not deploy these devices with their factory software. Instead, we have long standardly replaced it with the secure, verified, and open-source ROOter Golden Orb firmware.
⚠️ The Threat: “ENDLESSDOORS” Backdoor (CVE-2026-66747)
Security experts have identified an embedded malicious implant dubbed ENDLESSDOORS. This backdoor is present across virtually every published build of the Zbtlink factory firmware across their entire product range (including WE, WG, and CPE series models).
How does this backdoor operate?
- Process Masking: The malicious code triggers immediately upon system boot and runs under the name
kworker. This is a deliberate attempt to blend in with legitimate Linux kernel threads and evade basic detection. - Phone-Home Beaconing: The device does not open any external listening ports that a firewall might flag. Instead, it actively initiates an unencrypted TCP connection to a hardcoded Command-and-Control (C2) server roughly every 35 seconds.
- Full Root Control: When the remote C2 server responds, it grants the attacker an interactive shell with the highest possible privileges (
root/uid=0). Because the communication channel is entirely unauthenticated and unencrypted, anyone capable of intercepting or hijacking the network path can easily gain full remote code execution on the router.
Due to the severity of this design flaw, the vulnerability has been assigned a near-maximum severity rating of CVSS 9.3 (Critical).
✅ Why Our Customers Are 100% Protected
Our core philosophy is to deliver solutions that are not only high-performing but fundamentally secure. For this exact reason, our provisioning process always involves completely wiping the factory software from the hardware.
In its place, we flash the advanced ROOter Golden Orb firmware:
- Zero Malicious Footprint: ROOter Golden Orb is built on top of a clean, community-vetted OpenWrt base. It completely eliminates all proprietary, closed-source Zbtlink software packages—including the compromised
librctl.sobinary responsible for the ENDLESSDOORS implant. - Total Transparency: Every process running within our deployed firmware is fully transparent and auditable. There are no hidden “phone-home” routines communicating with external third-party servers.
- Enhanced Performance & Features: Beyond absolute security, Golden Orb provides our clients with vastly superior cellular (LTE/5G) modem management, advanced routing capabilities, and rock-solid long-term stability.
💡 Summary
If your router was purchased, configured, and deployed by our team with Rooter firmware, then you do not need to take any action or worry about this vulnerability. Your device was fully immunized against this factory flaw before it ever connected to your network. If you run the factory OpenWRT firmware, then please replace it by Rooter firmware immediately. It is availabel for free for download or we can send it to you upon request.
Should you have any technical questions regarding this advisory or wish to verify the firmware status of a specific deployment, please do not hesitate to reach out to our technical support team.